ISO/IEC 27001:2022 Certification 

Information Security Management Systems Certification 

Demonstrate effective management of customer data and secure information with certification to the international ISO 27001 standard.

Get ISO Certified
Transfer Certification
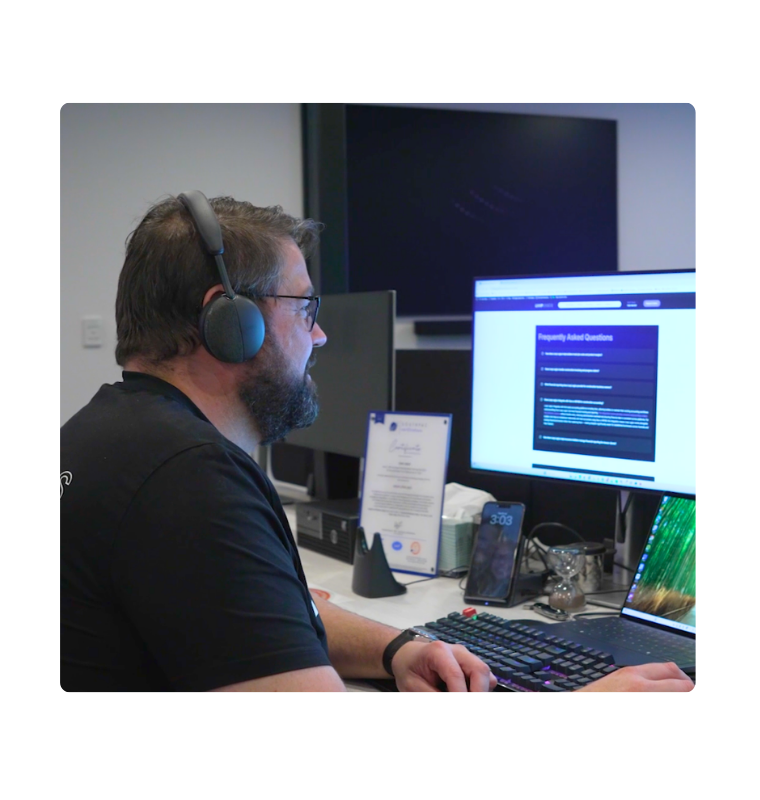
Lead Auditor Conducting an On-Site Audit at a Client’s Office in Burleigh Heads, QLD ISO 27001 Information Security Management System Badge
Southpac_Hero_BG_OceanBlue-3
Build Trust, Secure Data

Why get ISO 27001 Certification?

Information security management has become an increasing consideration for modern businesses looking to keep their digital information secure.

Whether it’s to benefit from best practice or to reassure customers and clients that the global standard in recommendations has been followed, getting certified to ISO 27001:2022 will support any organisation’s cyber and data security management systems.
Auditor Reviewing Information on a Tablet in Burleigh Heads, QLD Southpac Certification Background Network
How we help with ISO 27001 Certification

Information Security Management System Certification

Whether you're getting certified for the first time, upgrading to the ISO 27001:2022 standard or looking for a new certification partner – we're here to support you with a fresh approach to certification.

ISO 27001:2022 Certification

Get accredited certification to ISO 27001:2022 Information Security Management Systems with Southpac Certifications to manage the security of any kind of digital information for your organisation.

Transferring your ISO 27001 certification

Tired of the same old audits from your current provider? We've built our reputation around Certification Differently – taking a fresh approach to management systems certification.

Transferring your ISO 27001 certification is easier than you think. Contact us at any stage in your current audit cycle. 

inlineCTA-blue
Case Study - Loop Logics - InlineCTA
 
ISO 27001 Case Study

How ISO 27001 Certification helped Loop Logics secure more Tier 1 clients

See how software provider, Loop Logics, has strengthened information security processes, built client trust and secured larger clients with ISO 27001 certification.

ISO 27001 Frequently asked questions

What is ISO 27001?

ISO 27001:2022 is the international standard for an information security management system (ISMS) used to manage the security of assets such as financial information, intellectual property, employee details, and information entrusted by third parties.

Who needs ISO 27001 certification?

ISO 27001:2022 certification is suitable for organisations of any size or sector that need to effectively manage the security of sensitive data, demonstrate rigorous cyber security controls, and ensure regulatory compliance.

What are the benefits of becoming ISO 27001 certified?

The benefits of achieving ISO 27001:2022 certification include enhanced information security, compliance with legal and regulatory requirements, increased credibility and trust with customers and partners, and a competitive advantage in the marketplace.

How do I start the process of ISO 27001 certification?

To begin the certification process, your organisation needs to implement an information security management system (ISMS) that complies with ISO 27001:2022 requirements. This involves designing and implementing processes and procedures that address risk management, asset protection, and incident response to secure your information assets.

What does the ISO 27001 certification process involve?

The ISO 27001 certification process involves two stages: Stage 1 is a documentation review, and Stage 2 is an onsite audit. Following your initial certification, your auditor will return for a surveillance audit in years 2 and 3, followed by a re-certification audit the following year to commence the cycle again.

How do I update my certification from ISO 27001:2013 to ISO 27001:2022?
If your organisation is certified to ISO 27001:2013 and wants to upgrade to ISO 27001:2022, start by familiarising yourself with the key updates in the new standard. Ensure your ISMS documentation and processes align with the new requirements. Conduct an internal audit to verify compliance, and then contact Southpac Certifications to schedule an audit for the new standard.
What is required to maintain ISO 27001 certification?
Maintaining ISO 27001 certification requires ongoing compliance with the standard, including regular internal audits, annual surveillance audits, and a re-certification audit every three years. Southpac Certifications supports you through this continuous improvement process.

Trusted by leading companies across Australia, New Zealand and the Asia Pacific

Southpac Certifications Background
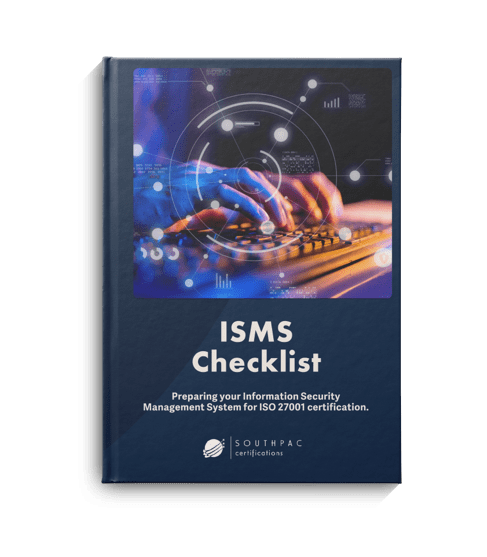
Free ISMS Checklist in Southpac Certifications Burleigh Heads, QLD
 
Free ISMS Checklist

Get ready to achieve ISO 27001 certification

Determine the elements you have in place or need to implement to prepare your Information Security Management System for certification to ISO 27001.

A partner in your ISO 27001 Certification

Supporting you every step of your ISO 27001 Certification journey

We take a fresh approach to ISO certification, becoming a partner in your growth and success. At Southpac Certifications, our focus is on continuous improvement for our clients’ long-term success, rather than an annual tick and flick approach.

interview

Before

Our coordination team work tirelessly to understand your business and certification needs, from urgent proposals through to accommodating specific requests, and scheduling audits with an understanding approach.

personal-trainer

During

You'll be assigned a Lead Auditor who will be your main point of contact throughout the process, and beyond – supporting you as you move forward to the assessment and certification of your management system.

event-confirm 1

After

Throughout the three-year certification cycle, our team will be available to support with any challenges or questions that may arise outside of the annual audit. That’s the added value of Certification Differently.

Accredited Certification in Australia & New Zealand

Strengthen Data Protection with ISO 27001 Certification

Achieving third-party certification to ISO 27001:2022 provides external stakeholders with the assurance that your organisation meets the international standard for Information Security management and data protection. 

Arrow Icon
Streamline

Maintain an ISMS that works in the context of your organisation.

Meter Icon
Improve

Achieve better security performance that drives customer satisfaction.

Communicate Icon
Demonstrate

Lead the conversation around data security with your customers. 

Access Icon
Access

Secure contracts with government and clients that prioritise data security. 

Increase Icon
Increase

Maximise trust and reputation to build market share in your industry.

Ready to get started?

Discover Certification Differently with us

We've built our reputation around Certification Differently – taking a fresh approach to management systems certification.
Southpac Certifications Employees in Burleigh Heads, QLD
Related Resources

Learn more about ISO 27001 Certification

Ready to get started?

Get a quote for Information Security Management Systems certification

Get a Quote
Transfer Certification